Knowledge Network · Apr 1, 2026
The 2026 Cisco breach vs. 2020 SolarWinds (Sunburst): An Analysis
The 2026 Cisco breach and the 2020 SolarWinds (Sunburst) incident are both "hallmark" supply chain attacks, but they represent different generations of the same threat. While SolarWinds targeted the build process of a fi...
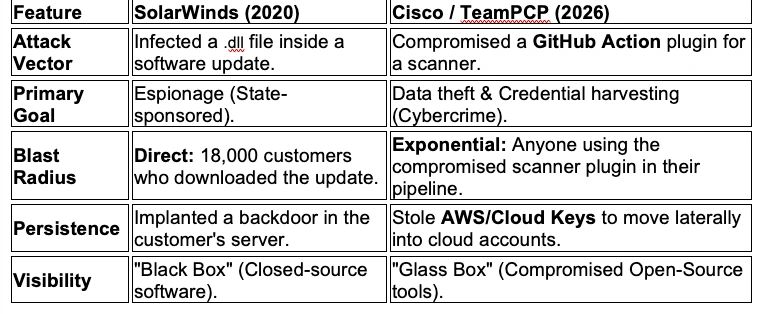
Here is how the two incidents compare:
- Technical Similarities: Both attacks focused on "poisoning the well" rather than attacking a target's front door.
- Subversion of Trust: In both cases, the attackers compromised a "trusted" source. For SolarWinds, it was a legitimate software update. For Cisco, it was a trusted security scanner (Trivy) and its GitHub Action plugins.
- Targeting the "Kitchen," Not the "Meal": Neither attack started by exploiting a bug in the final software (like a firewall or a router). Instead, they compromised the development environment—the "kitchen" where the software is cooked.
- Dwell Time & Stealth: Both actors showed a preference for staying quiet. In SolarWinds, the malware (Sunburst) stayed dormant for up to two weeks before activating. In the Cisco incident, the attackers (TeamPCP) used stolen credentials to blend in with normal developer activity, making them much harder to spot than a typical virus.
Key Differences: 2020 vs. 2026
The industry has moved from "On-Prem" software to "Cloud-Native" development, and the attacks have evolved to match.
Summary for Defenders
The biggest lesson connecting these two is that "Signed Code" does not equal "Safe Code." In SolarWinds, the malware was signed with a real certificate. In the Cisco attack, the malicious plugin was running inside a "trusted" workflow.
From Third Party Threat Hunting™ (TPTH™)
Put it to work
Privileged access
The free VAULTS™ training: 31 minutes on privileged access review, with a worked review.
Get the free training →Have us run it
Managed third-party threat hunting: practitioners on your systemically critical vendors, automation on the rest.
See the managed tiers →