Oct 27, 2026
The New TPRM Proposal Drops the Checklist. Now What?
The 2026 interagency TPRM proposal drops the contract checklist. Examiners will weigh reasonable decisions, so your files must show the reasoning.
Insights
Analysis, frameworks and field notes from TPTH™ engagements, plus outtakes from the podcast. Everything here comes out of real client work.
Oct 27, 2026
The 2026 interagency TPRM proposal drops the contract checklist. Examiners will weigh reasonable decisions, so your files must show the reasoning.
Oct 21, 2026
Continuous monitoring only helps if it leads to action instead of alert fatigue. The practical fix is to tie alerts to ownership and thresholds. Different teams should only see the vendors they are responsible for, and n...
Oct 20, 2026
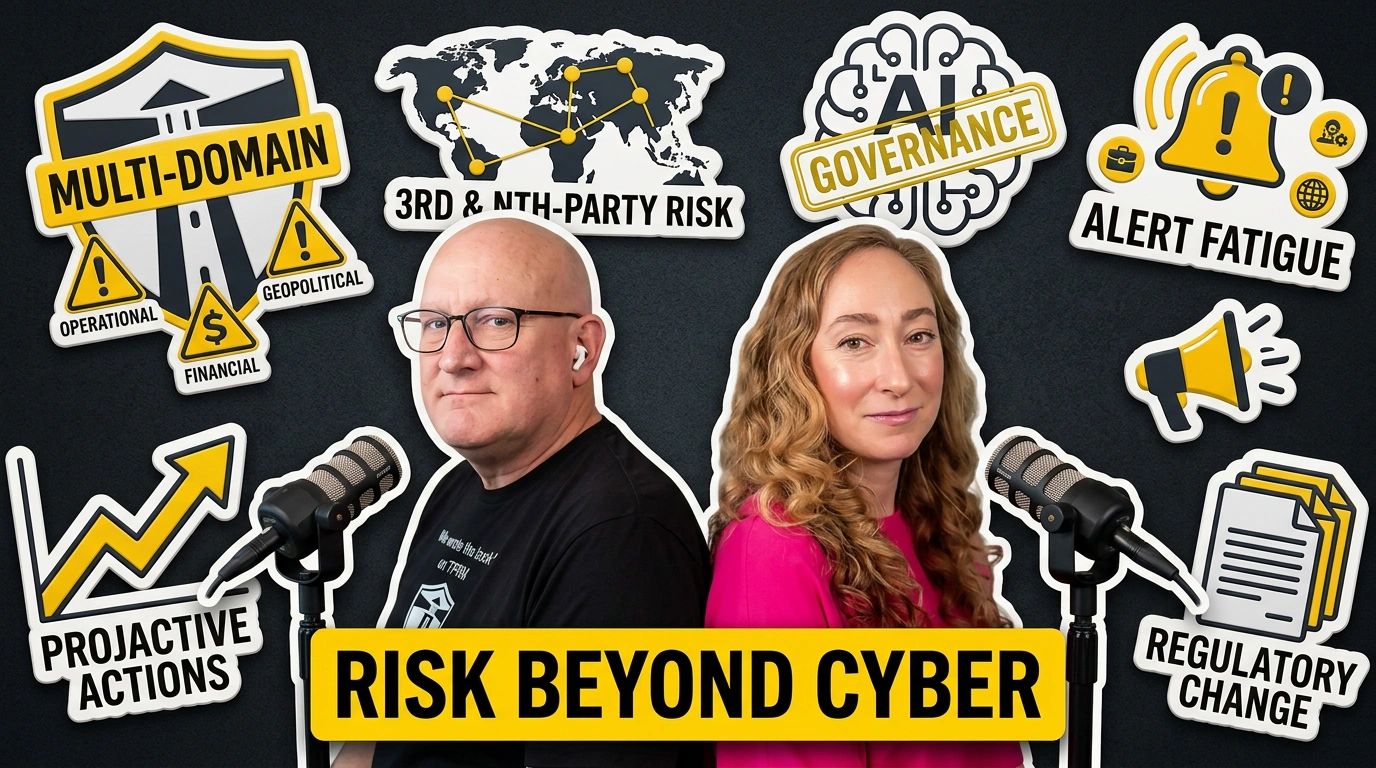
Third-party risk management is changing fast because supply chains are more fragile, vendors move quicker, and disruptions stack across cyber, operations, finance, ESG, and geopolitics. A traditional vendor risk assessme...
Oct 7, 2026
Frameworks help because they give teams shared language and a repeatable yardstick. Common references like the OWASP Top 10 for LLM Applications and Cloud Security Alliance guidance help establish taxonomy, but they are ...
Oct 6, 2026
Third-party AI risk is moving faster than most enterprise vendor risk management programs can keep up with. As organizations embed generative AI in customer support, coding, analytics, and internal search, many of those ...
Oct 1, 2026
Between audit cycles, security posture degradation often shows up as drift. Control drift includes reduced MFA coverage, growth in privileged accounts, gaps in endpoint or backup coverage, failing evidence, and unresolve...
Oct 21, 2026
Continuous monitoring only helps if it leads to action instead of alert fatigue. The practical fix is to tie alerts to ownership and thresholds. Different teams should only see the vendors they are responsible for, and n...
Oct 20, 2026
Third-party risk management is changing fast because supply chains are more fragile, vendors move quicker, and disruptions stack across cyber, operations, finance, ESG, and geopolitics. A traditional vendor risk assessme...
Oct 7, 2026
Frameworks help because they give teams shared language and a repeatable yardstick. Common references like the OWASP Top 10 for LLM Applications and Cloud Security Alliance guidance help establish taxonomy, but they are ...
Oct 6, 2026
Third-party AI risk is moving faster than most enterprise vendor risk management programs can keep up with. As organizations embed generative AI in customer support, coding, analytics, and internal search, many of those ...
Oct 1, 2026
Between audit cycles, security posture degradation often shows up as drift. Control drift includes reduced MFA coverage, growth in privileged accounts, gaps in endpoint or backup coverage, failing evidence, and unresolve...
Sep 30, 2026
AI That Actually Helps TPRM: Brian Shaw on Where Automation Works (and Where It Doesn't Yet)
Sep 29, 2026
Third-party risk management is breaking under the weight of “point-in-time” thinking. A SOC 2 report, annual audit, or perfectly completed security questionnaire can look like proof of safety, but it mainly proves prepar...
Sep 25, 2026
Alert fatigue is another concrete pain point. Security ratings, threat feeds, and “signal providers” can generate endless alerts without telling you what to do next. The episode argues for risk-based prioritization tied ...
Sep 24, 2026
Third-party risk management (TPRM) often looks mature on paper while staying fragile in practice. Security teams grill employees with identity and access management controls, but treat vendors with production access like...
Sep 23, 2026
When you work with managed service providers and other high-access vendors, you are not just buying a service - you are extending your enterprise into someone else’s environment. That makes MSP security due diligence a d...
Sep 21, 2026
Most security teams are asking vendors the wrong question. Not "are you compliant?" Ask: "can I actually trust how you operate? “I asked Bill Haber about third-party risk, MSPs, and AI. His answer was blunt: A lot of s...
Sep 17, 2026
One of the strongest parts of the conversation was Mike’s blunt take on old due diligence habits. He was clear that the classic “send a questionnaire, wait for a reply, file it away” model is not enough anymore. In fact,...
Sep 16, 2026
The biggest shift right now is not that third-party risk matters more - it is that the consequences are changing. Mike explained that sanctions, export controls, and national security enforcement are increasingly where r...
Sep 15, 2026
If you still think third-party risk management is mostly about onboarding questionnaires and annual reviews, you are already behind.In this conversation with Mike Volkov, a former federal prosecutor turned compliance att...
Sep 15, 2026
Beyond the Vendor Questionnaire: What Mike Day Taught Us About Fourth-Party Risk
Sep 15, 2026
AI is accelerating the redesign of third-party risk assessment frameworks and best practices. Automation and AI-powered TPRM tools can convert static questionnaires into continuous monitoring by pulling near real-time ev...
Sep 11, 2026
A recurring theme in the interview was the control assurance paradox: a vendor can pass an annual audit, hand over a clean SOC 2 Type II report, and still become the source of a breach.That is not because the report is u...
Sep 11, 2026
Theory is good, but production-ready code is better. The final post in the series invites security engineers, architects, and threat hunters to bridge the gap between AI concepts and real-world execution.
Sep 10, 2026
How do you build an agent that scans external surfaces without causing self-inflicted outages or running out of scope? This technical deep-dive focuses on Agent 1—the Recon Agent.
Sep 10, 2026
Third-party risk management is hitting a breaking point: teams face resource constraints while vendor ecosystems explode, and leadership asks for more than cybersecurity alone. Beyond cyber risk, modern vendor risk now i...
Sep 9, 2026
One of the most useful ways Becky framed the topic was by pushing back on the idea that third-party risk management belongs entirely to audit or security.Her answer was clear: it is neither one by itself.Audit is great a...
Sep 9, 2026
The Governance Disconnect
Sep 9, 2026
When a new zero-day hits the news, security teams usually face chaos, endless meetings, and manual asset mapping. This post walks through a real-world case study comparing traditional response workflows against a SAM-ena...
Sep 8, 2026
This is part 2 of a 5-part series that will detail how Third Party Threat Hunting™ is offering a new course that will provide a path to proactive threat hunting for zero-day vulnerabilities in your third-parties. To neut...
Showing the 24 most recent of 98 posts.
Tools
For vendors already approved, already contracted and already assessed. Each question with the reason it is asked, what a good answer looks like, and what a non-answer looks like.
Read the six questions →