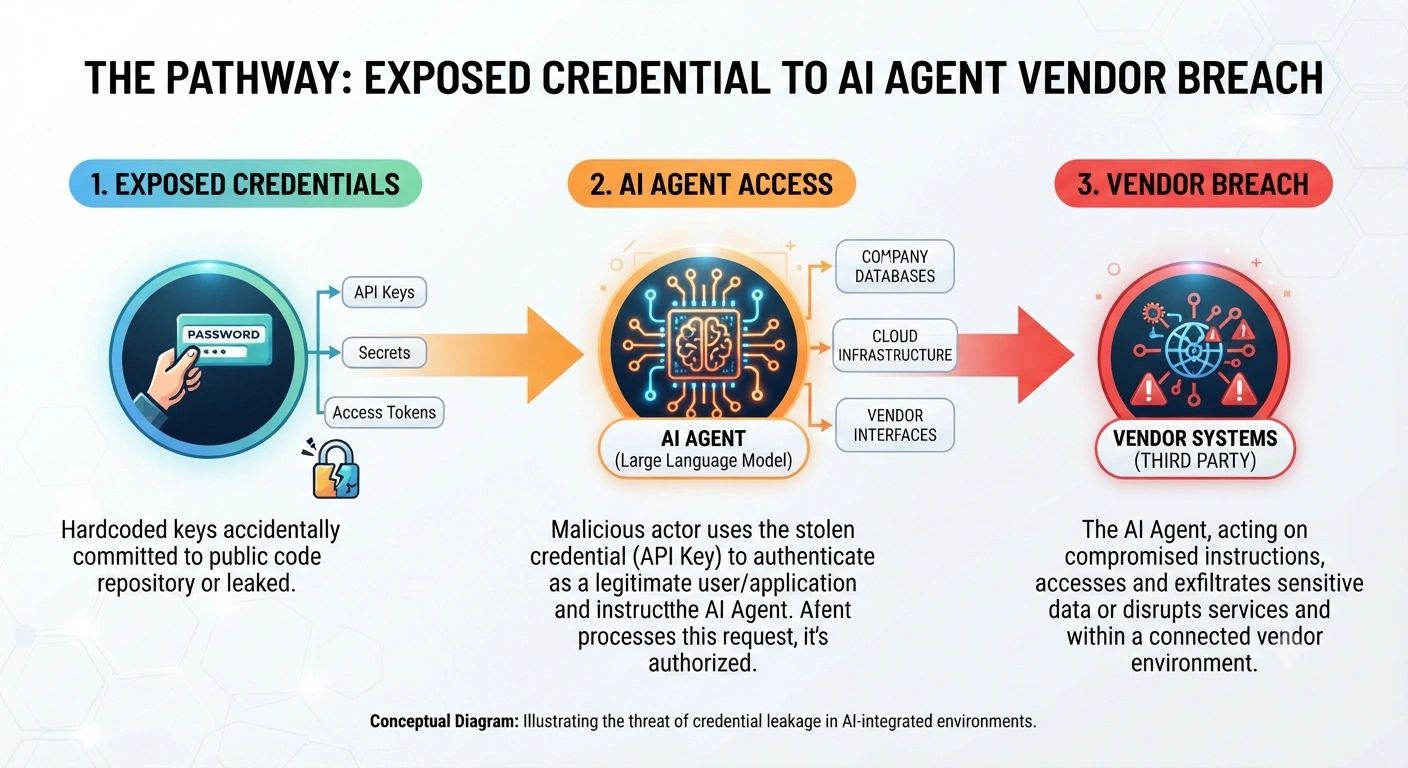
From a recent episode of Third Party Threat Hunters:
When an AI agent can autonomously find a weakness, bypass safeguards, and exploit an exposed system, third-party risk stops being a paperwork problem and becomes an active defense problem. In this conversation, Greg sits down with Clarence Chio, co-founder and CEO of Coverbase, to talk about why the future of third-party security will be defined by automation, humility, and threat-hunting thinking - not annual questionnaires alone.Clarence argues that the industry is at an inflection point. The old model assumes vendors answer questions honestly and that a point-in-time review is enough. But modern attackers - including AI agents - don’t care about your questionnaire cadence. They exploit access, stale credentials, hidden integrations, and fast-changing environments. If you manage vendor risk, this episode is a useful wake-up call and a practical roadmap for what to do next.
To learn more, go to my podcast and subscribe: https://thirdpartythreathunters.buzzsprout.com
####
From Third Party Threat Hunting™ (TPTH™)
Put it to work
Privileged access
The free VAULTS™ training: 31 minutes on privileged access review, with a worked review.
Get the free training →Have us run it
Managed third-party threat hunting: practitioners on your systemically critical vendors, automation on the rest.
See the managed tiers →